Cybersecurity threats are rising in frequency and sophistication, which calls for the enhancement of better, real-time threat detection systems. This paper introduces a cyber threat intelligence (CTI) platform that combines a deep learning-based detection model with real-time log analysis with the utilization of security information and event management (SIEM) systems. A deep neural network trained with stochastic gradient descent (SGD) is at the heart of the proposed gadget, which uses log data to detect malicious activity. Logs are collected and consumed from the Wazuh platform, permitting real-time correlation and possibility tracking. A tailored dashboard presents a friendly interface for visualizing alerts and designs. The suggested structure mixes detection precision, machine scalability, and functioning responsiveness in changing network environments. Experimental outcomes demonstrate that the model is highly accurate and responsive in determining dangers, structuring its feasibility for real-time business environments.
Turn pages by dragging a corner, clicking a page, or with the ← → keys.
Loading article…
Open the PDF instead
DOI: https://doi.org/10.63328/IJRDES-V7CIP14
OpenYou've reached the end of this article.
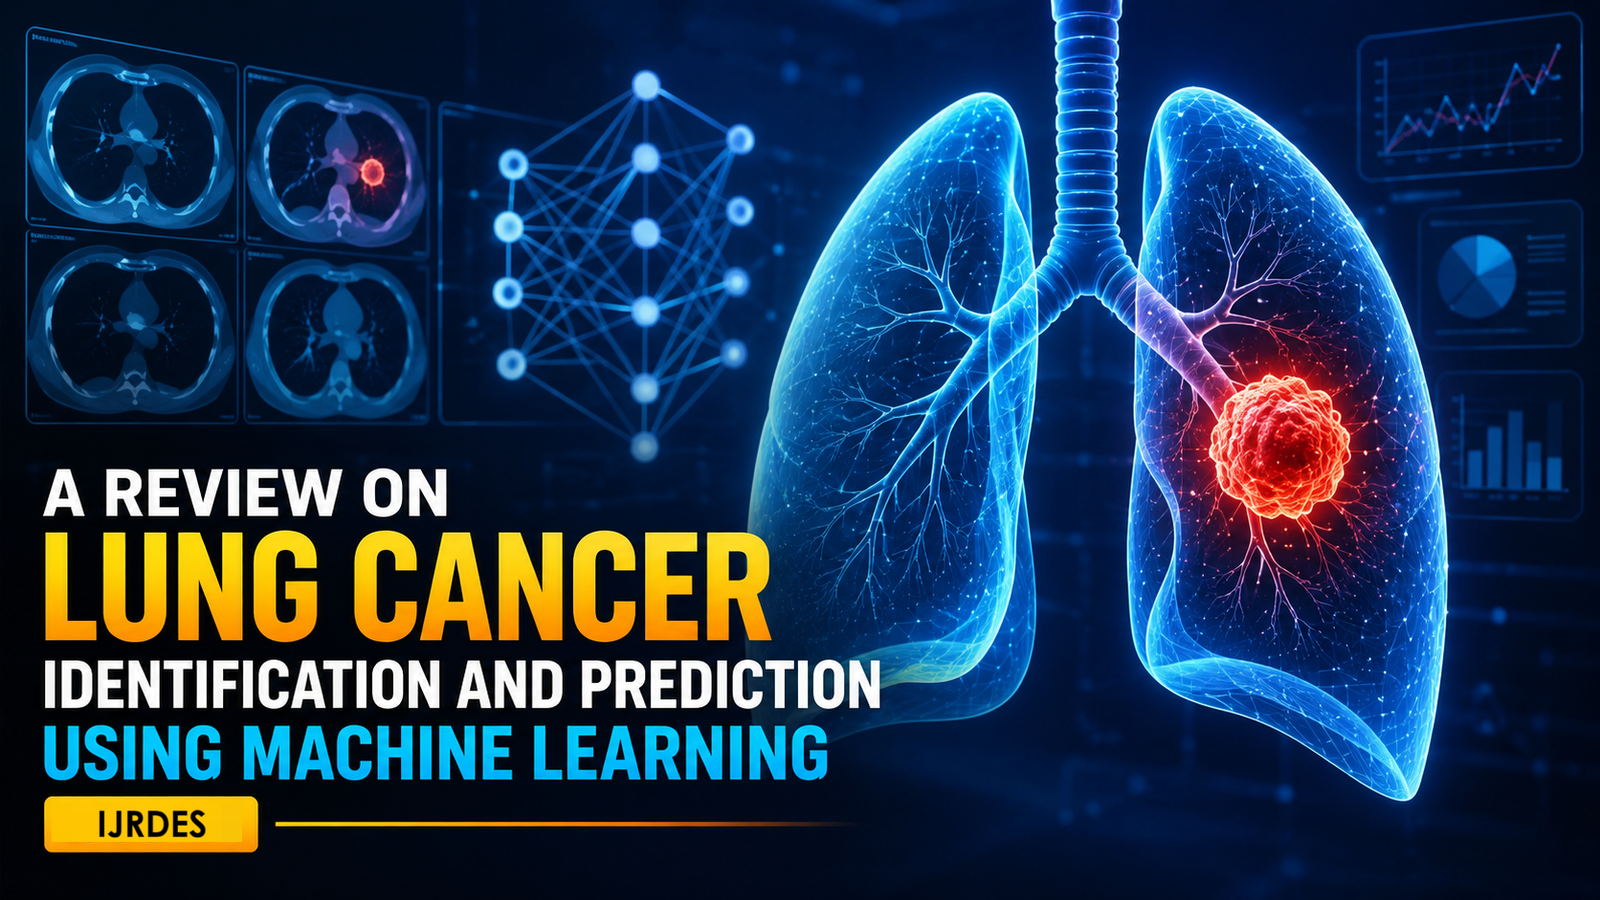
Lung cancer is accountable for more deaths each year than all of the other leading cancers - breast,...
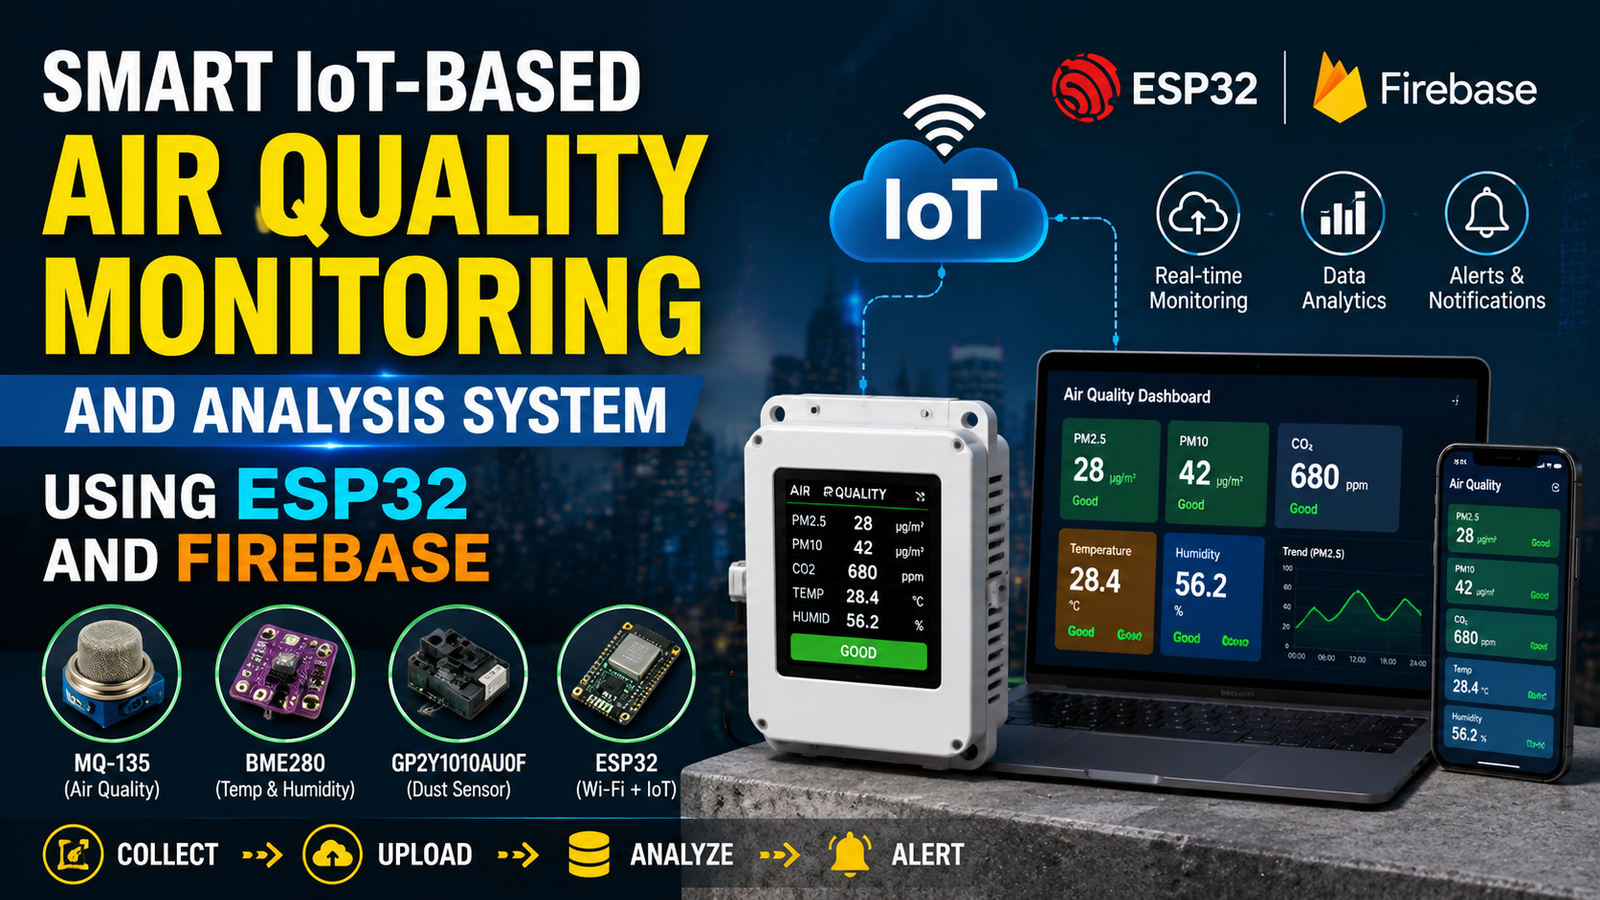
The growing rates of air pollution are both highly hazardous to the human environment and health, an...
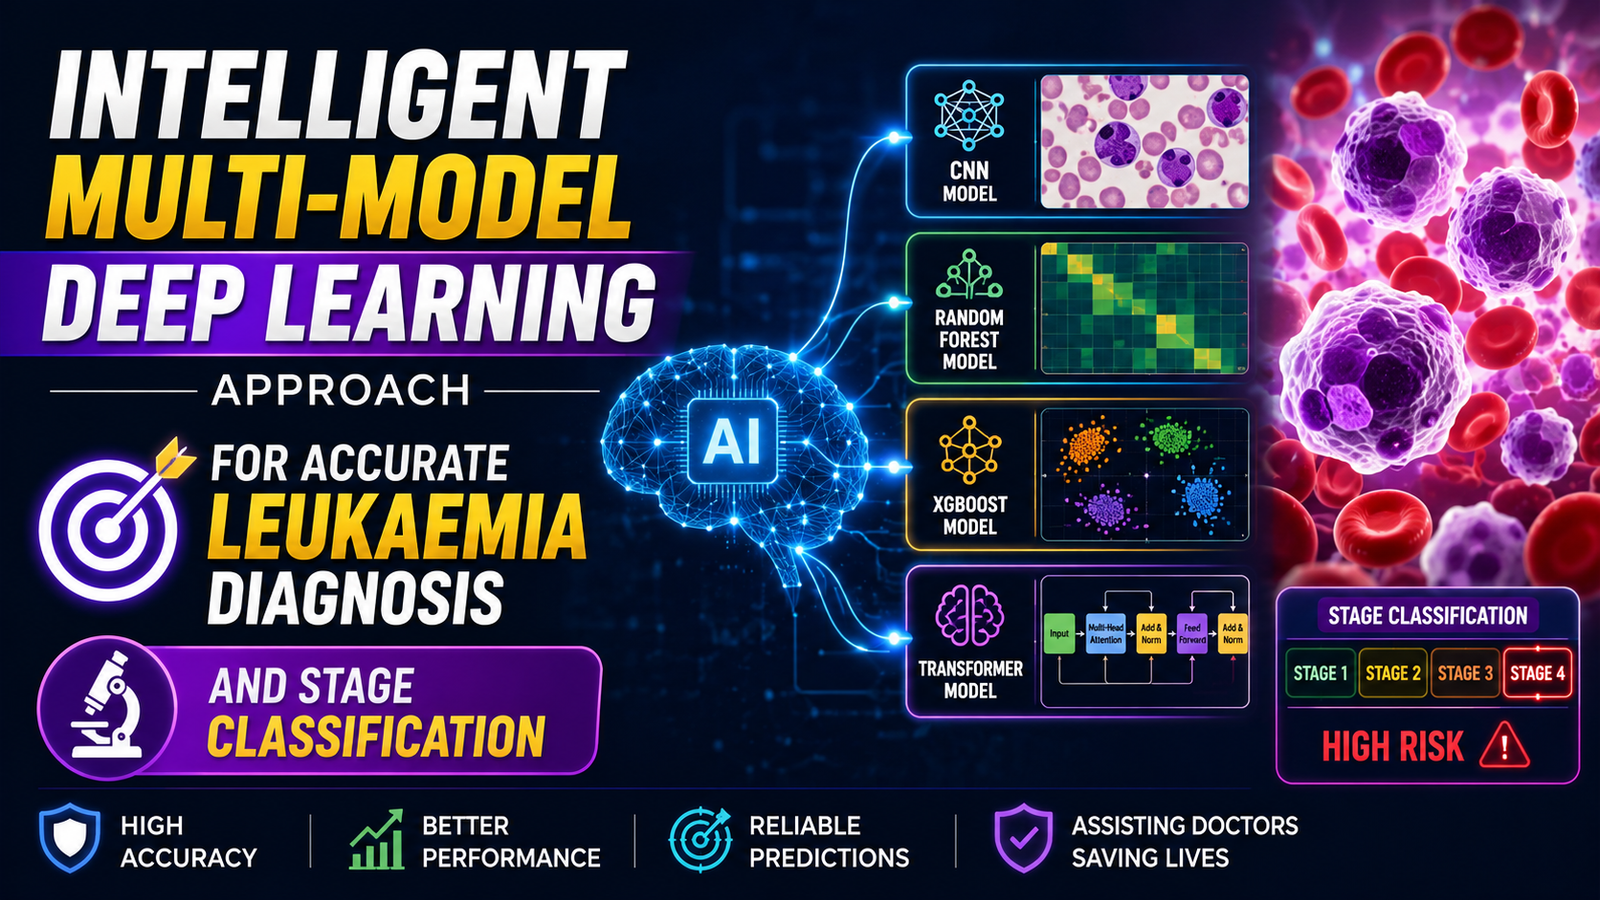
Leukaemia, a malignant disorder of the blood and bone marrow, requires early and accurate detection ...
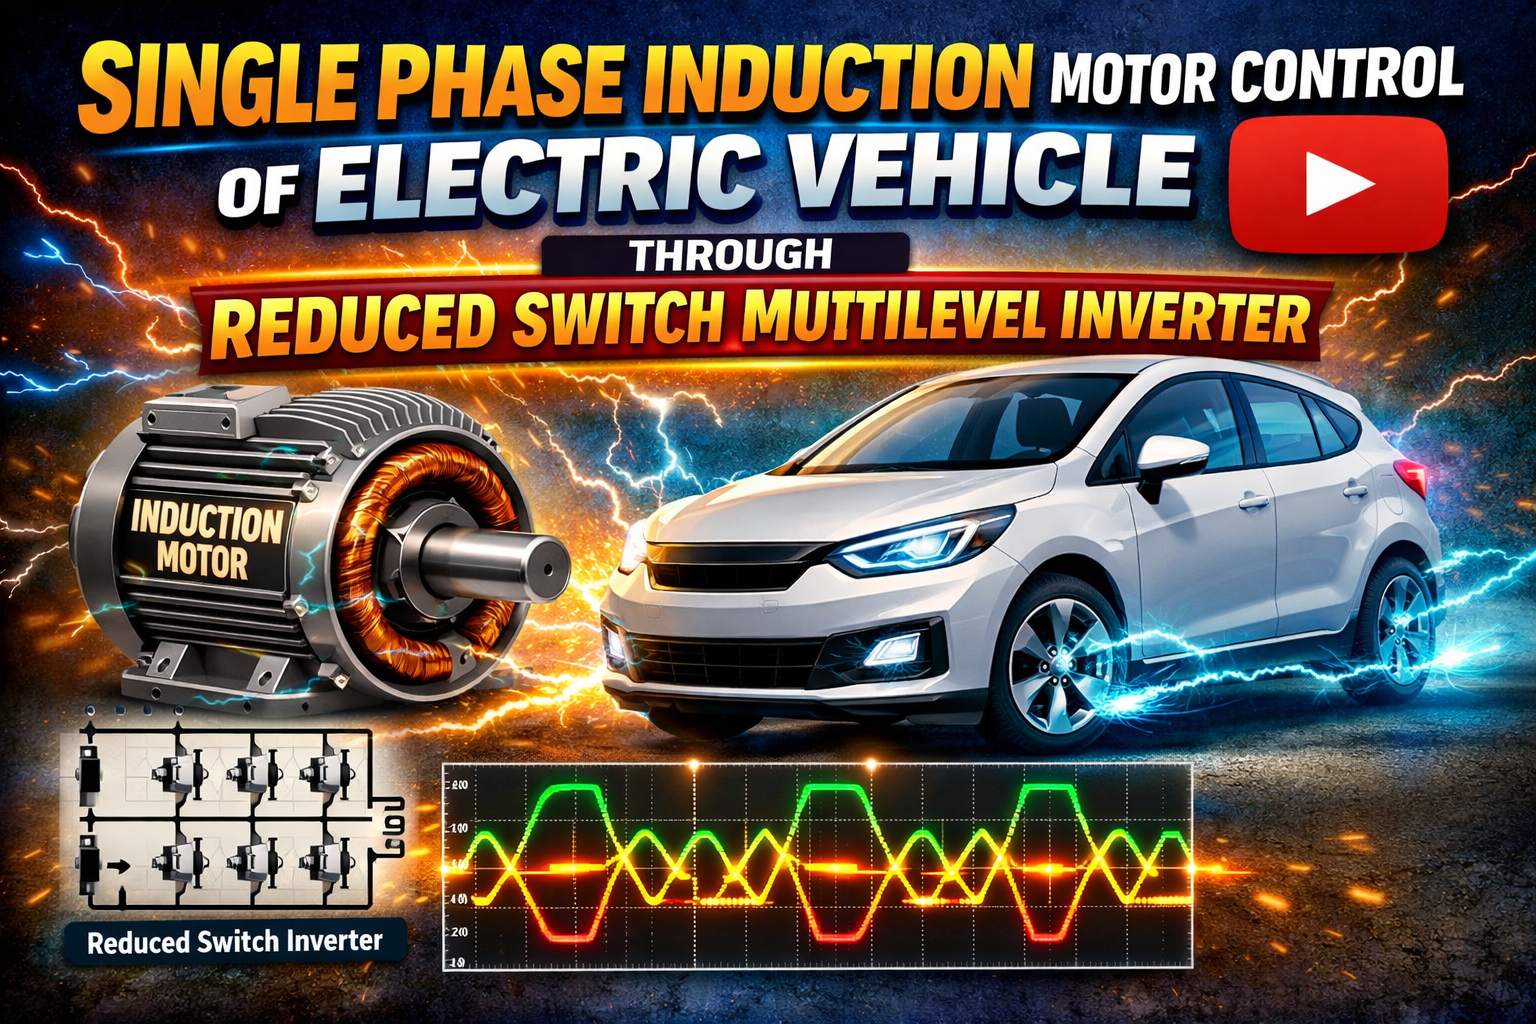
Multilevel inverters (MLIs) have gained an increasingly high profile in the area of power electronic...